Bintang Nathaniel Satria Putra
Cybersecurity Student at BINUS University
I'm a cybersecurity student at BINUS University specializing in digital forensics and a member of PETIR.
Beyond competing in national CTFs and authoring CTF challenges, I build security tools and work as a Security Operation Center (SOC) L1 Intern to tackle real-world security incidents.
Jakarta, Indonesia
01
Education
2024 – 2028 (expected)
BINUS University
S.Kom
- Relevant coursework: Computer Security Fundamental, Network Pentest, Mobile Pentest, Computer Forensics, Reverse Engineering, Binary Exploitation
- Applied STRIDE and MITRE ATT&CK frameworks to perform comprehensive threat modeling and risk mitigation for university application architectures.
current GPA 3.63 / 4.00
02
Experience
February 2025 – Present · Jakarta · Hybrid
Security Operation Center (SOC) L1 Intern
PT Maxplus Indonesia Anugrah
- Conduct proactive security monitoring and log analysis using SIEM solutions (e.g., Splunk, Wazuh, etc) to identify and triage potential network threats.
- Perform vulnerability assessments to pinpoint infrastructure weaknesses and collaborate on technical project folders for remediation tracking.
- Analyze network traffic and investigate security alerts to ensure incident readiness and robust defense mechanisms.
Burp SuitePythonSIEMLog AnalysisThreat HuntingVulnerability Assesment
03
Projects
 Featured
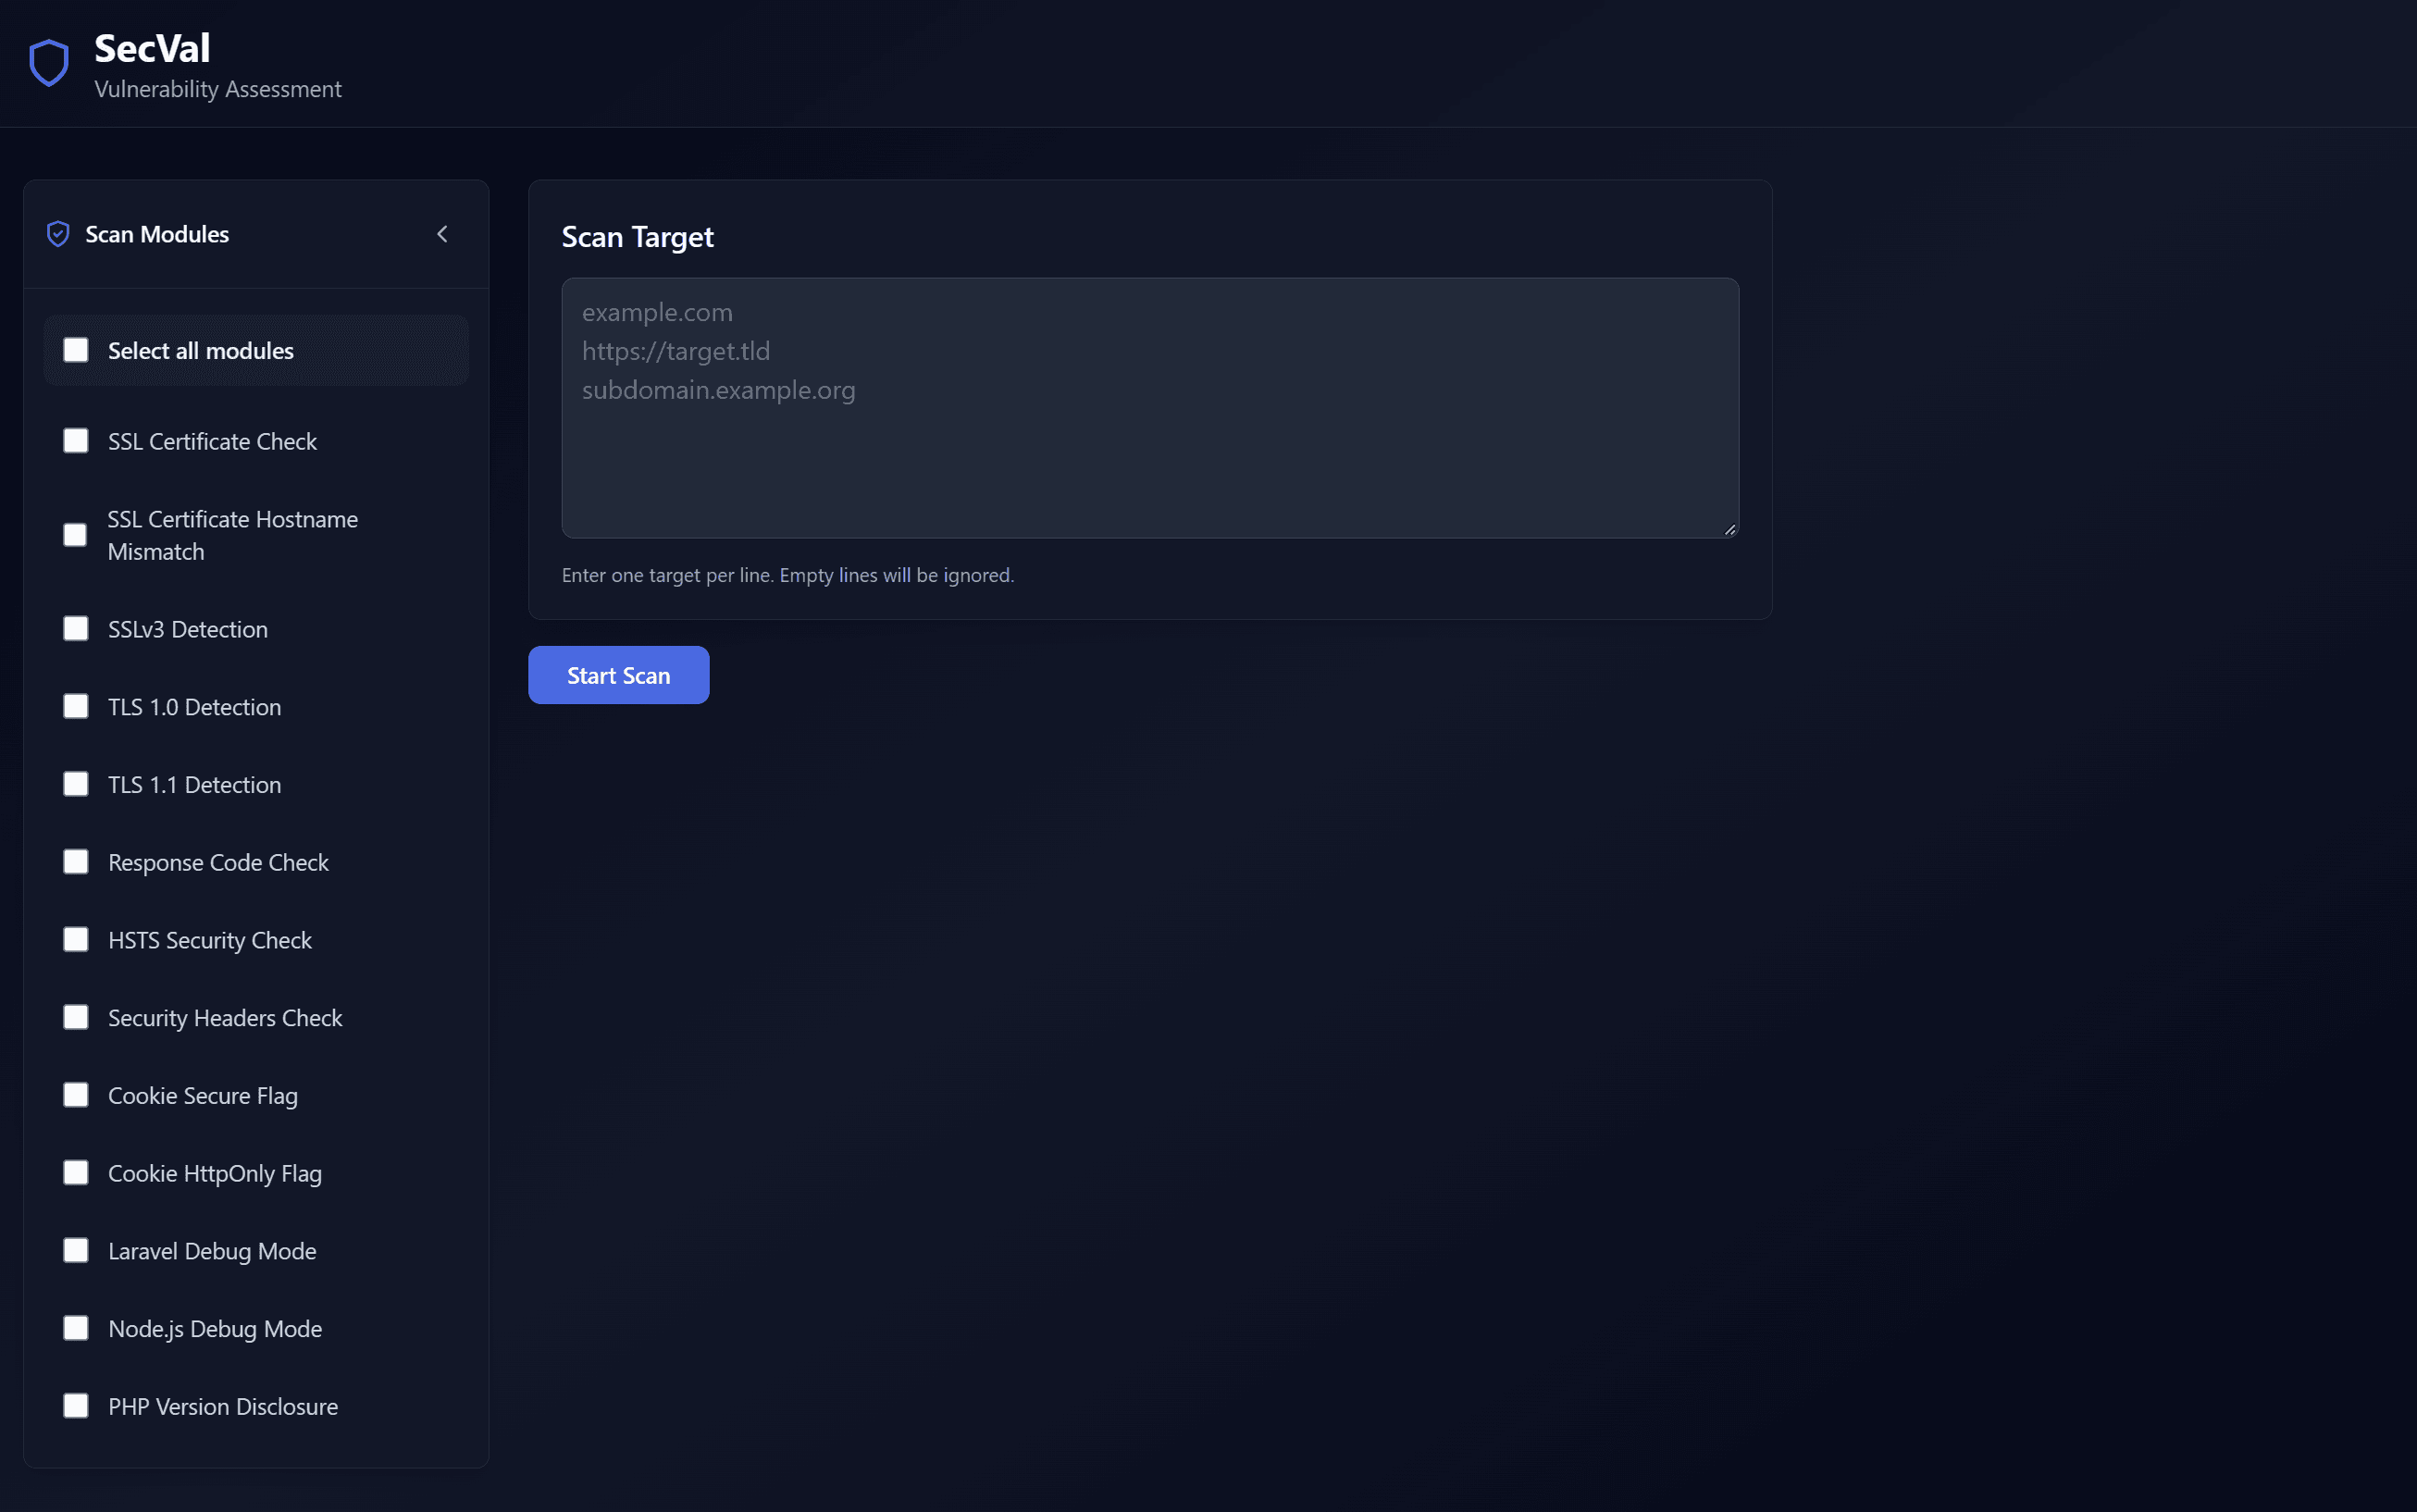
Security Validator
SecVal is a web application security scanner that checks whether a website exposes common vulnerabilities or insecure configurations. It is modeled on the scanning tools used in vulnerability assessments.
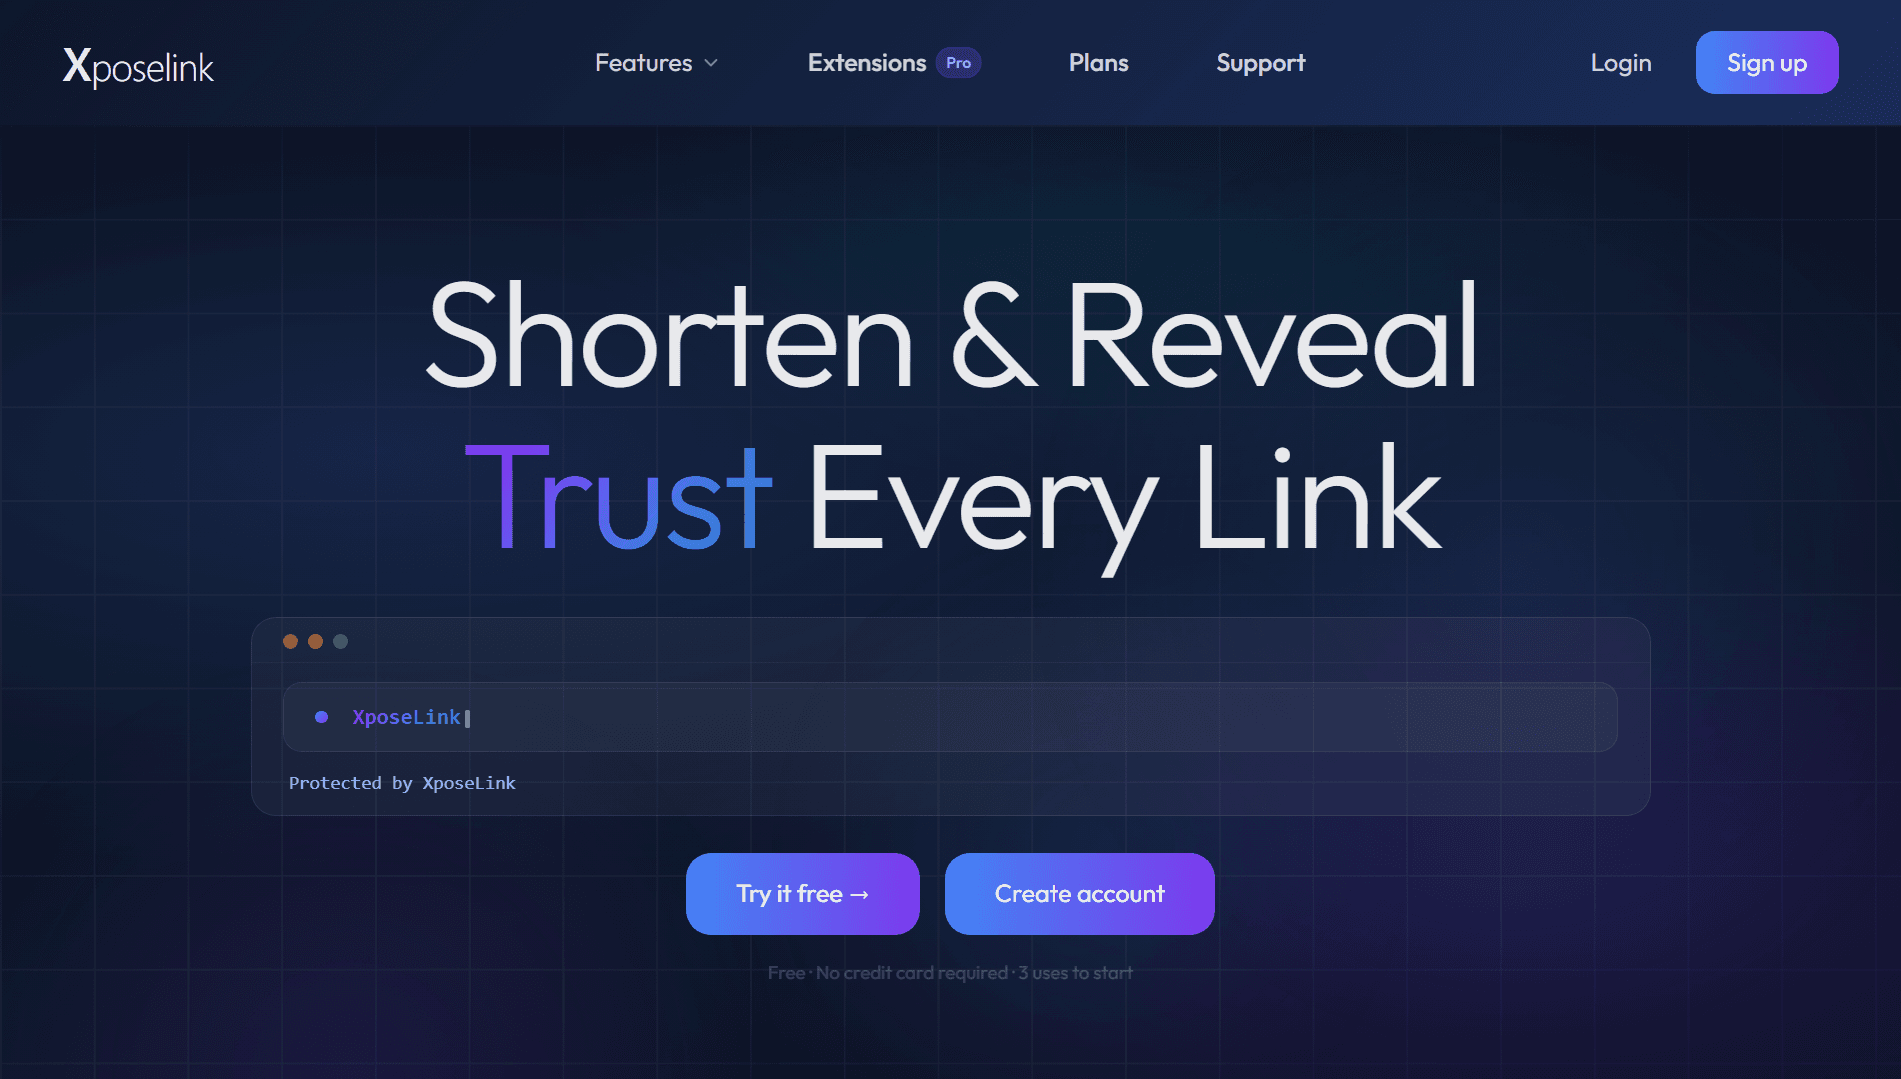
XposeLink
XposeLink is a URL shortener — it takes a long link and turns it into a short one that's easier to share. I led the planning side: mapping out how the system should work, identifying what could go wrong security-wise, and organizing the team's work schedule.
Locker
Authored an easy network forensics and malware analysis challenge for National Cyber Week (NCW) Qual 2025.
8x8
Authored an easy misc challenge about audio steganography for PETIR Regeneration 2026.
Ngik
Authored a medium forensics challenge covering Android disk and malware analysis for PETIR Regeneration 2026.
DpDp
Authored an easy forensics challenge on DisplayPort traffic analysis using Wireshark for TECHFEST 2026.
Ghost of BeeCTF
Authored a hard forensics challenge combining Linux memory, disk, and malware analysis for BeeCTF 2026 Final.
04
Achievements
Overall Champion · 2026
Overall Champion — PLAY IT Cyber Combat 2026
Politeknik Negeri Malang
- Awarded to BINUS University as the top-scoring institution in the university-level division.
- Earned from the combined results of its campus representatives rather than a single team.
Dokumentasi1st Place · 2026
PLAY IT Cyber Combat 2026
Politeknik Negeri Malang
- Two-stage national competition: a jeopardy-style qualification round, then an Attack & Defense final where every team defends an identical stack of vulnerable services while exploiting the same weaknesses on their opponents.
- Patched live bugs without breaking the SLA checks that keep a service scoring — a different discipline than the qualification round rewarded.
- Read opponent traffic to recover exploits aimed at us and turn them back around.
- Took away that real defense is mostly triage: deciding which bug to fix first when every minute of downtime costs points.
Dokumentasi1st Place · 2026
Best Attacker PLAY IT Cyber Combat 2026
Politeknik Negeri Malang
- Ranked 1st for Best Attacker in the Attack & Defense final, awarded for the strongest offensive performance against opposing teams' services.
- Automated exploits into scripts that fired every round instead of landing a shell once by hand.
- Re-targeted quickly as teams patched the easy paths, with the scoreboard making it immediately clear which assumptions about a target were wrong.
Dokumentasi2nd Place · 2026
The ACE 2026
Universitas Diponegoro
- Jeopardy-style qualification round, followed by a final pairing boot2root machines with face-to-face team rounds.
- Ran the full intrusion chain end to end on the boot2root stage — enumeration, initial foothold, then privilege escalation to root — where every step builds on the last, unlike isolated jeopardy challenges.
- Split work across the team under the time pressure of the face-to-face rounds, where calling when to abandon a dead-end path mattered as much as technical skill.
DokumentasiValid Duplicate · 2026
Valid Vulnerability Discovery & Disclosure
Indonesian Local Government (Target Redacted)
- Reported a critical unauthenticated SQL injection — a ts_rewrite bypass on the datastore_search_sql API (CVE-2026-42031 / CVE-2026-42032) — on 18 August 2026.
- Triaged as valid but closed as a duplicate.
Finalist · 2025
IFEST 2025
Universitas Atma Jaya Yogyakarta
- Jeopardy-style format across both stages, advancing through the qualification round to reach the national final.
- Worked the forensics track, where the final's challenges spanned audio steganography, memory forensics, and a light OSINT component — a wider set than the qualifiers had called for.
- Did not place, but the unfamiliar categories drove the self-study that became my strongest area: I went on to author audio steganography and memory forensics challenges of my own.
05
Organizations
2025 – 2026
Cyber Security Community
Activist of Education
Researched and produced articles and social content on current cybersecurity news, distilling technical incidents into material the wider student community could act on.
July 2025 – July 2026
BINUS University
Freshmen Leader & Partner
Mentored incoming freshmen through their transition into university life, facilitating orientation sessions that relied on public speaking, leadership, and one-on-one communication.
2026 – 2027
Cyber Security Community
Chief Compliance Officer
Oversee internal policy to keep the organization's programs within legal, regulatory, and ethical boundaries, reviewing events and initiatives for compliance before they run.
2026
Cyber Security Community
General Manager at EXPO CSC
Directed logistics, booth layout, and task delegation for university-wide EXPO events across the Kemanggisan and Alam Sutera campuses, driving student recruitment and community engagement.
06
Skills
07
Goals & What's Next
Complete all PortSwigger Web Security Academy labs to master advanced web exploitation.
Achieve recognized industry certifications and conquer Machine boxes on Hack The Box.
Secure impactful bug bounties on HackerOne by hunting critical vulnerabilities.
Deepen digital forensics and incident response (DFIR) skills via CyberDefenders platform.